A breach discovered after close does not care whose watch it happened on, and I have never seen a deal team price a risk they weren't shown. It becomes the acquirer's liability. The regulatory exposure follows. So does the write-down.
Cyber due diligence is an inherent part of the M&A process. It runs ahead of the acquisition to drive the deal. Its findings must flow directly into the transaction itself.
I have sat through cyber due diligence that never gets there. It produces a checklist of findings rated high, medium, and low, then hands it to a deal team negotiating in dollars.
The gap between a severity rating and a deal structure adjustment is where acquirers overpay. The fix is to treat the target's cyber exposure the way finance treats receivables: as a quantified figure that belongs in the model. Putting a financial value on that exposure gives the deal team a direct lever across purchase price adjustments, escrow holdbacks, specific indemnities, and post-close remediation budgets.
TL;DR
In an acquisition you buy the target's breaches too, priced or not. Cyber risk is a valuation input. A process that returns severity ratings instead of financial figures is not sufficient due diligence.
In M&A, cyber risk is measured by the impact on the business, on the value the business can generate, and on the likelihood that an attack disrupts revenue and operations enough to stop the acquired organization generating value for its owners. Modeling the attack paths to the target's business-critical assets is how that impact gets priced. Each path carries a Cost of Breach times Likelihood of Breach figure, and every finding becomes a deal-negotiation line item.
Integration creates exposure that neither company carried alone. Connecting two networks opens attack paths that existed in neither environment alone. Model the combined surface before day one.
Why Standard M&A Security Checklists Leave Millions in Hidden Risk
A checklist tells you what is wrong with the target, but a deal team cannot act on that list. They need the cost those problems would impose on the combined company.
Real acquirers already price that distinction into deals. When Yahoo disclosed two historic breaches during its acquisition by Verizon, the parties cut the purchase price by 350 million dollars (TechCrunch, 2017).
When Marriott acquired Starwood, it also inherited a compromise of the Starwood reservation database that had gone undetected since 2014. It was only surfaced in 2018, and drew a regulatory penalty measured in the tens of millions (Hunton Andrews Kurth, 2020).
In both cases the risk was live before close.
Verizon priced it and cut the purchase price. Marriott closed without adjusting for the exposure it had just inherited.
Price reductions represent only one available lever. The exact same risk figure dictates:
How much capital gets locked in escrow
What binding remediation SLAs enter the purchase agreement
Where specific indemnities must replace blanket representations
A weak cyber posture shifts the deal structure toward protective measures.
A finding you cannot price is a finding the deal team cannot negotiate against. A checklist that flags a critical vulnerability on the target's billing platform and a critical vulnerability on its marketing site treats them as equal, when the dollar exposure behind each is wildly different.
The billing platform protects revenue the company depends on.
The marketing site protects little more than a blog. The severity score treats them the same. Pricing each in dollars exposes the real gap between them.
The Four Attack Paths Every Acquirer Should Model Before Signing
Every acquisition carries risk through a small number of recurring attack paths. The work is to map the realistic routes an attacker would take to the target's business-critical assets, then price each with Cost of Breach times Likelihood of Breach.
1. Regulated-Data Path
The route to systems holding PII, PHI, or financial records subject to disclosure obligations. A breach here triggers regulatory notification, potential fines, and reputational damage that can exceed the direct incident cost. This is the path most standard due diligence looks for first.
Stolen or compromised customer PII was involved in 52% of breaches (IBM, Cost of a Data Breach Report 2026), and the regulatory penalty for mishandling it has outgrown the category of operational cost. GDPR enforcement alone has issued more than five billion euros in cumulative fines since 2018 (DLA Piper, 2025), with individual cases running into the hundreds of millions.
2. Revenue-Critical Path
The route to billing, payment, or order-processing systems whose disruption costs revenue directly. Ransomware landing here does not require a data theft to impose a material loss.
Recovery from a ransomware event on a production system runs past one and a half million dollars on average in direct costs, before any ransom payment (Sophos, State of Ransomware 2025).
3. Identity Pivot
Over-permissioned service accounts or shared credential stores that let an attacker move laterally from a low-value entry point to a high-value target. These rarely surface on a checklist because each finding is unremarkable in isolation. The value is in the chain.
The use of stolen credentials has shown up in almost a third of breaches over the past decade (Verizon, 2024 DBIR). The risk is in what they connect to.
4. Cross-Contamination Path
The attack paths that only exist once the two networks connect. The target exposure becomes the acquirer exposure on integration day. Standard due diligence stops at the target and misses this entirely, because it does not exist until integration begins.
How to Turn Cyber Findings Into a Deal-Negotiation Line Item
Once each path carries a dollar figure, every finding resolves into a deal lever. The framework is Remediate, Mitigate, or Accept, and each option carries a cost the deal team can put on the table:
Remediate. Price the fix and require it as a condition of close or a post-close remediation SLA, for the paths on a direct route to a high-value asset.
Mitigate. Cost a compensating control, such as segmentation isolating the target's network until integration is validated, where a full fix cannot land before close.
Accept. Document the residual exposure with its dollar amount and carry it into the model as a known, quantified liability, for paths low enough to absorb.
Each decision maps to a specific transaction lever. (1) Direct price reductions: Unmitigated breach liabilities or legacy incidents directly reduce enterprise value and purchase price. (2) Escrow holdbacks: Escrow reserves are used to provide a targeted cash buffer against potential liabilities. (3) Reps & warranties / specific indemnities: Having an exact dollar figure makes it easy to prove risk to insurance companies and deal teams. Use it to get special coverage for specific risks and define what the seller must pay for if something goes wrong. (4) Post-close integration budgets: Instead of just listing technical security fixes, turn them into clear budget line items. This gives the team a solid post-close fixing schedule and sets aside the exact money needed to complete those repairs.
A material residual exposure becomes an escrow holdback or a specific indemnity in the reps and warranties.
The Cye platform supports this directly through What-If Analysis. Before the deal team commits to a position, the platform models what each option changes. It shows how much expected loss the option removes and which validated paths it closes. It also shows what residual exposure remains.
The acquirer can then negotiate against that evidence.
Why Your Integration Plan Needs a Combined Attack-Path Model Before Day One
Integration is where an acquisition manufactures new risk, because connecting the two networks creates attack paths that existed in neither company on its own.
Due diligence typically assesses the target, then plans integration as a later, separate phase.
That sequence hides the most important exposure. The day the networks connect, an attacker who lands on a target endpoint may have a route into the acquirer's own business-critical assets, a path that did not exist while the companies were separate.
Modeling the combined network graph before close surfaces it.
I have watched integration teams discover that exposure only after the networks were already connected, well past the point where a dollar figure could still shape the deal structure through escrow, indemnities, or price adjustments.
Fixing this requires viewing the acquirer and the target as a single combined network before day one. Instead of assessing the target company in isolation, you map the buyer's IT environment and the target's IT environment together. You trace which weak points on the target side actually open a route to the buyer's critical assets, then put a dollar figure on those specific paths. That turns post-close integration from an IT guessing game into a clear financial decision.
Apply Gartner's continuous threat exposure management, CTEM, discipline: (1) scope the merged surface, (2) map the assets and connections across both environments, and (3) validate which findings sit on a live path to an asset that matters. Cyber risk quantification then prices that validated map.
This surfaces the exact weak points on the target side that open a direct route into the buyer's critical data, allowing you to put a dollar figure on those paths before signing.
How the Cye Platform Models the Combined Surface
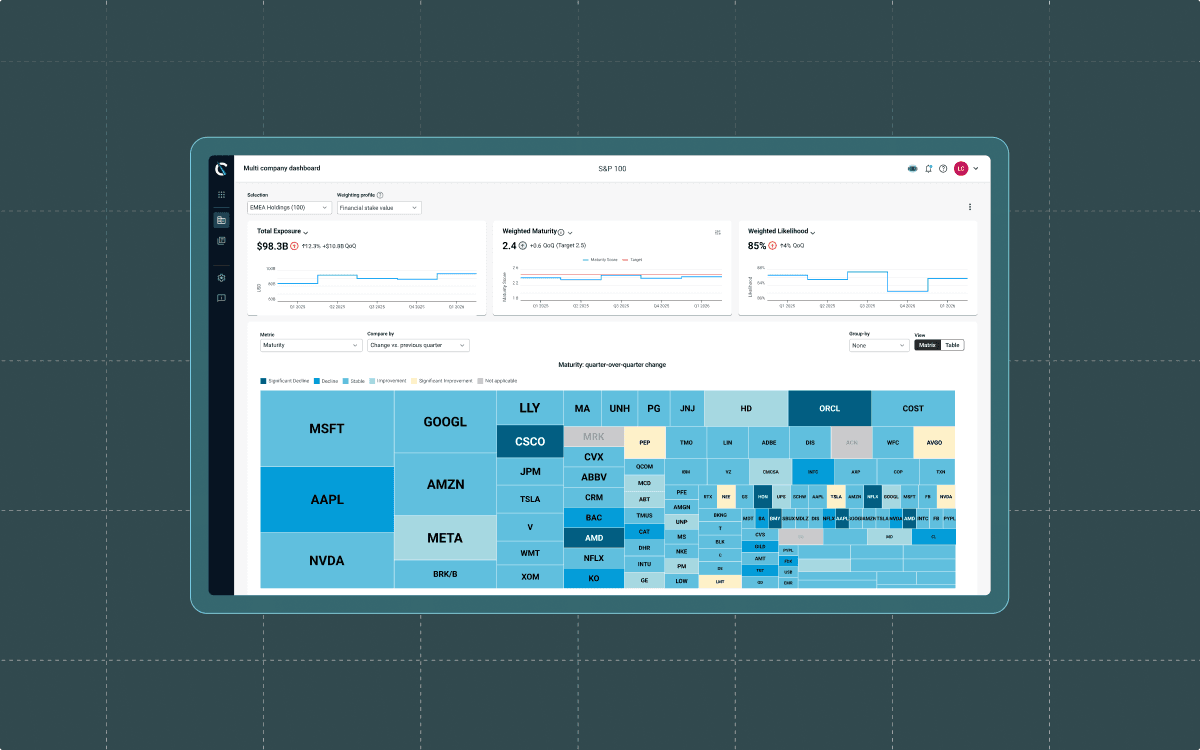
Cye's AI-native exposure management platform runs this across the merged environment, mapping every asset and connection and pricing each validated path with CoB × LoB so the integration plan carries a priced exposure at every stage.
Cye's Org Attack Graph maps every asset and connection across both environments, then models the attack paths that emerge once the two networks connect. Each asset in the merged surface is benchmarked against the Industry Attack Graph, so the deal team sees how the combined environment compares with sector peers rather than a view of the target alone.
As integration progresses and the network changes, the exposure model updates. The deal team does not inherit a static snapshot taken at close. They carry a live model that tracks which paths are open, what each costs, and what the decision is for each one.
The acquirer should know, before signing, which of its own critical assets become reachable from the target the moment integration begins. The combined network graph turns integration from an IT project into a priced risk decision.
You can test Cye’s model and estimate the potential cost of a breach and its business consequences for your organization using Cye’s online Cost of Breach Estimator. It only takes a few minutes.
A Worked Example: The Liability a Checklist Misses
The two approaches diverge on the same finding. This is an illustrative model. No specific client is behind it, but the pattern is one that attack-path modeling surfaces routinely.
A target runs a vendor portal that a scanner rates medium severity. On a checklist it sits mid-list, unremarkable.
Attack-path modeling asks a different question. What can an attacker reach from that portal? The answer is that the portal shares credentials with an internal service, which connects to the billing system that processes the target's invoiced revenue, which in turn holds the customer records that trigger regulatory disclosure if breached.
Three individually unremarkable findings chain into one route to material, regulated data.
Priced with Cye’s Cost of Breach times Likelihood of Breach model, that single path can carry a multimillion-dollar expected loss, while the checklist reported a medium.
Attack-path modeling converts technical issues into a clear financial figure that moves directly into the deal mechanics, shaping escrow requirements, remediation SLAs, and baseline valuation adjustments.
How to Build a Due Diligence Process That Prices Every Risk
A due diligence process that produces dollar figures runs in a fixed order, and it fits inside a standard diligence window when it is scoped to the assets that matter.
1. Scope Business-Critical Assets First
Identify the systems whose compromise would trigger contractual penalties or regulatory fines. Include any system whose compromise would cost the company revenue directly. Model these before anything else.
Pricing the assets that carry the exposure does not require a complete inventory first.
Cye's platform maps each asset to the relevant NIST CSF functions automatically. Its cost model already accounts for the data an asset holds (including PII, payment, and health records) and the regulatory fines a breach of that data would trigger. As a result, the due diligence team sees which systems carry disclosure-driven exposure.
The platform's maturity scoring (calibrated against a global industry benchmark of 2.35 on a 0 to 5 scale) places the target's security program against sector peers from the first day of diligence.
A program scoring low in the Protect function means the acquirer cannot rely on the target's defensive controls when calculating residual exposure.
2. Map Likelihood of Breach Per Attack Path
Validate which paths to those assets are reachable and exploitable, which produces the probability side of the calculation.
3. Apply Cost of Breach Per Asset
Two approaches dominate standard practice.
Qualitative models classify each finding on a scale: critical, high, medium, low, and organize those findings into a heat map.
FAIR (Factor Analysis of Information Risk) goes further, modeling risk as loss event frequency times loss magnitude to generate a probability distribution in dollar terms.
Both run into the same constraint in early-stage diligence. Each requires historical loss data from the target organization to calibrate the model. An acquirer rarely has that data at the stage where a dollar figure would still move the deal.
Cye's model draws on more than 250,000 real-world breach events, with a documented fit of 93% of the variables that determine a breach's final cost (Cye). It is calibrated by industry, geography, organization size, and more. That external dataset gives a defensible starting figure in early-stage diligence. That sharpens further as the acquirer gains access to the target's own environment data, where Cye can point its model at the organization’s specific environment.
4. Tag Each Finding: Remediate, Mitigate, or Accept
This converts the technical report into a negotiation input.
A Remediate finding lands as a condition of close or as a post-close SLA with a penalty clause if the fix misses its deadline. A Mitigate finding maps to an escrow holdback sized to the control cost plus the residual exposure it does not fully cover. An Accept finding converts to a specific indemnity in the reps and warranties, sized to the quantified dollar figure.
Every line item on the tagged list has a corresponding lever, and the deal team negotiates from a number, not a severity label.
5. Deliver a Dollar-Exposure Report Alongside the Technical Report
Standard diligence reports deliver a heat map and a written technical narrative. The heat map sorts findings by color. The narrative describes what each finding is. Neither translates into a valuation line item, and there is no mechanism in either output that lets the deal team put a number on the table.
A financial figure is a different artifact. It travels from the security assessment directly into the financial model, and from the financial model into the deal room.
The exposure figure is wider than a single number.
Cye’s model covers both financial cost and reputational damage. It adds operational impact too, such as lost pipeline and customer trust.
For enterprises above $5 billion in annual revenue, reputational loss accounts for roughly 60% of total expected breach cost, based on Cye's analysis of real breach data. This is why a report that captures only direct incident cost understates what the acquirer is buying.
That figure still has to reach the board in a form they can act on. Cye generates a board-ready report and PPT deck from the target's own validated environment data, so the dollar figure that priced the deal-room discussion is the same figure that goes into the board presentation.
In my experience, boards negotiate against dollar figures. A severity count never gets read past page one. A dollar figure gets read by everyone at the table from the deal team up to the board, denominated in dollars.
Cyber risk is a valuation input: price it before signing
Every deal team that closes without a financial exposure figure inherits the same problem Marriott did. The problem is an asset whose breach cost is real whether or not it was modeled. The difference between Verizon and Marriott came down to one thing. One side saw the number before signing. The other found it after.
Cye turns attack-path findings into that number, having quantified over $20 billion in exposure across 500+ organizations and analyzed more than 1 million attack paths.
The platform maps the target business-critical assets on its Org Attack Graph, validates which paths reach them, and prices each with Cost of Breach times Likelihood of Breach.
The model prices each path as a distribution of expected loss, not a single point estimate. The deal team receives both a central figure and the confidence range around it.
That range feeds the entire deal economics: enterprise valuation adjustments, escrow holdbacks calibrated to the target's cyber posture, post-close CapEx allocations, and risk-transfer terms.
Using this model, cyber posture serves as a foundational driver of total deal structure.
Frequently Asked Questions
The questions deal teams and acquirers most often raise about pricing a target's cyber risk before close.
What is the difference between a vulnerability scan and attack-path modeling in M&A due diligence?
A vulnerability scan lists the target's weaknesses and rates each by technical severity. Attack-path modeling maps which of those weaknesses chain into a reachable route to a business-critical asset, then prices the route. A scan produces a severity list. Attack-path modeling produces a dollar figure the deal team can negotiate against.
How do you estimate the Cost of Breach for a target before you have full access to its data?
Cost of Breach draws on an actuarial dataset of more than 250,000 real-world breach events across industries and organization sizes, adjusted for the target's specific factors such as sector, data types, and revenue.
Because the model rests on external breach data, a defensible dollar figure is possible early in diligence, before the acquirer has access to the target's internal history.
The figure is then refined as access to the target's environment increases.
Should an acquirer remediate cyber findings before close or hold back escrow?
It depends on the dollar exposure and the timeline. A finding on a direct route to a high-value asset usually warrants remediation as a condition of close or a binding post-close SLA.
A material residual exposure that cannot be fixed before close is better handled as an escrow holdback or a specific indemnity sized to the quantified figure.
The decision is a negotiation, and a dollar exposure per finding makes it one.
Can attack-path modeling be completed inside a 30-day due diligence window?
Yes, when the modeling is scoped narrowly to the target's business-critical assets. The highest-value modeling covers the small number of systems whose compromise would materially affect the deal, and that work fits inside a standard window. Scoping by business impact first keeps the timeline realistic. Broad, unfocused discovery blows past it.
Which of a target's business-critical assets should be modeled first?
The assets whose compromise would move the deal: systems processing regulated data and platforms handling material revenue. It also includes anything whose breach triggers a disclosure obligation the acquirer would inherit. Model the paths to those first, price them, and expand the surface from there as the diligence window allows.
Further Reading
Cye, The Complete Guide to Cyber Risk Quantification: https://cyesec.com/blog/the-complete-guide-to-cyber-risk-quantification
Cye, The Complete Guide to Exposure Management: https://cyesec.com/blog/exposure-management
Understanding the 5 Stages of the CTEM Framework: https://cyesec.com/blog/ctem-framework
Cye, Cost of Breach Estimator: https://cyesec.com/cost-of-breach-estimator