
Resource Center
 Blog
Private Equity’s Expanding Attack Surface: Why Exposure Management Needs a New Approach
 Blog
5 Steps to a Board-Ready Cyber Risk Report
 Blog
Decision Velocity: The CISO Metric Nobody's Tracking (But Everyone Should Be)
 Blog
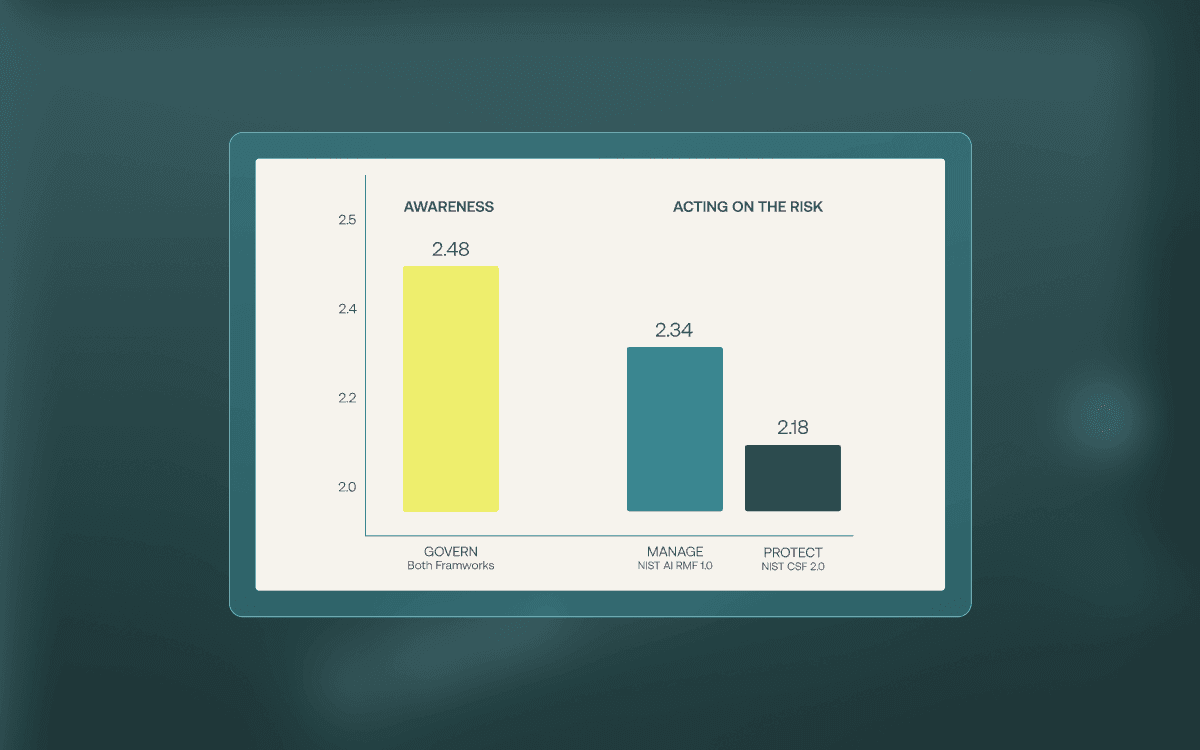
Can You Afford to Trust a Supplier's Word That Their AI Is Responsible?
 Blog
Cybersecurity Spending Is Rising. So Why Isn't Cyber Risk Falling?
 Blog
From Risk Reports to Operations: The Mandatory Phase of Cyber Risk Quantification to Drive Outcomes
 Blog
Why Cye: Competitive Comparison
 Blog
The Future of Security Investment Is Agentic
 Blog
Mythos is Breaking Traditional Cybersecurity. What Comes Next?
 Blog
Cye Appoints Dr. Nimrod Partush as Chief Innovation & AI Scientist
 Blog
The End of Siloed Security: How AI Is Transforming Group-Level Exposure Management
 Blog
AI and the End of Siloed Security
 Blog
Cye Recognized in Forrester Report: The Proactive Security Platforms Landscape, Q1 2026
- Blog
You Patch, They Browse
 Blog
GenAI and LLM Security: 4 Threats CISOs Can’t Ignore
 Blog
2026: The Year Cybersecurity Crosses Every Line
 Blog
Peak Revenue, Not Peak Risk: Instantly Map Your Black Friday Attack Paths
- Blog
The Essential Guide to Vulnerability Prioritization
- Blog
4 Ways Cye AI Helps CISOs Move as Fast as the Threats
- Blog
5 Key Takeaways from Our 2025 Cybersecurity Maturity Report
- Blog
Understanding the 5 Stages of the CTEM Framework
- Blog
Mitigation vs Remediation: What You Need to Know
- Blog
5 Active Directory Mistakes You Should Avoid
- Blog
The Threat Exposure Metrics CISOs Can’t Afford to Ignore in 2025
- Blog
Artificial Intelligence Is Just Math: Looking Beyond the Hype
- Blog
The Best 20 Cybersecurity Podcasts for CISOs’ Playlists
- Blog
The Complete Guide to Exposure Management
- Blog
Cyberattack Prevention: 11 Types and How to Avoid Them
- Blog
Cye Platform’s Game-Changing Upgrades: Redefining Cyber Exposure Management
- Blog
China’s Breach of U.S. Telecoms: A Cyber Wake-Up Call
- Blog
Top CISOs & Cyber Influencers Shine a Light on the Future of Cyber in 2025
- Blog
Navigating Challenges and Seizing Opportunities as a CISO in 2025
- Blog
Red Team vs. Blue Team Cybersecurity: They Can Help Your Business
- Blog
Mitigating Security Risks in Multi-Cloud Environments: Best Practices and Strategies
- Blog
DORA Is Coming: Are You Ready for the New EU Regulation?
- Blog
The Hidden Costs of a Cyberattack: The Impact on Reputation
- Blog
Software Updates and Malicious Code: The Paradox and Challenge
- Blog
Legacy Authentication: The Forgotten Back Door of Organizations
- Blog
The Interplay Between Physical Security and Cybersecurity in Organizations
- Blog
The Global Rise in Cybersecurity Regulations: Protecting Critical Infrastructure
- Blog
Mitigation at the Next Level: How Cye Platform Enhances Risk Management with ServiceNow and Jira
- Blog
The Complete Guide to Cyber Risk Quantification
- Blog
Cybersecurity Technologies and Their Role in Risk Optimization
- Blog
Navigating the Cybersecurity Landscape: An In-Depth Strategy Handbook
- Blog
Why FAIR Is Only as Good as the Data and Expertise It Relies On
- Blog
How a Cybersecurity Program Can Be a Return on Investment
- Blog
5 Key Insights and Lessons Learned from the CrowdStrike Outage
- Blog
Profit in Protection: Unlocking Key KPIs for Cybersecurity ROI
- Blog
Guardians of Security: Cybersecurity Governance Navigation as a CISO
- Blog
What 2024 Has Taught Us: Exploring Current Cybersecurity Trends
- Blog
The Importance of Assessing Cybersecurity Maturity: A Conversation
- Blog
Fortifying Defense: Red and Purple Teams and Risk Assessments
- Blog
4 Takeaways for CISOs About Breach Insurance Coverage
- Blog
Unraveling Uncertainty: The Art of Risk Mitigation Planning
- Blog
Mapping Progress: Exploring the Cybersecurity Maturity Model
- Blog
Briefing the Board: A CISO’s Guide to Cybersecurity Leadership
- Blog
Success Stories Unveiled: Achieving Effective Risk Mitigation
- Blog
The Recipe for Cybersecurity Maturity Using NIST CSF 2.0
- Blog
The Containment Playbook for Combatting Deep Fakes
- Blog
The Price of Not Following Application Security Best Practices
- Blog
How Advanced Technology and AI Play a Role in Cye Platform’s CRQ
- Blog
The Growing Threat of Cyberattacks and Social Engineering
- Blog
Mastering Cybersecurity Maturity: A Comprehensive Guide to Assessing Your Defenses
- Blog
The 23andMe Breach: Blame the User, But It’s Still Your Responsibility
- Blog
10 Best Practices for Operational Technology (OT) Security
- Blog
Tactical Edges: What My Dog Taught Me About Cybersecurity Strategy
- Blog
Latest Trends and Top Threats in the Ransomware Arena
- Blog
4 Key Tips for CISOs on Planning a 2024 Cybersecurity Budget
- Blog
How Cye Platform’s Cyber Risk Quantification Can Help Security Leaders (Infographic)
- Blog
The Role Experience Plays in Risk Mitigation
- Blog
Cybersecurity Predictions: What We Can Expect in 2024
- Blog
Cognitive Risk in the Boardroom: The Hidden Cyber Challenge
- Blog
The Israel-Hamas War’s Impact on the Cyber Threat Landscape
- Blog
The Top Cyber Threats Facing Consumers and Businesses Today
- Blog
How NIST and the SEC Align CISOs with the Board—and How CRQ Helps
- Blog
Too Many Trees in the Cyber Forest: Optimizing SIEM Systems and Monitoring Threats
- Blog
The Alarming Cyber Risks of ChatGPT
- Blog
The Importance of Threat Intelligence Monitoring in Cybersecurity
- Blog
Aligning with the New CISA Cybersecurity Strategic Plan
- Blog
Why the New NIST CSF 2.0 Transforms Cyber Risk Management
- Blog
What is Cyber Risk Optimization?
- Blog
6 Key Takeaways from the IBM Cost of a Data Breach Report
- Blog
6 Cybersecurity Risks Posed by Centralized Management
- Blog
Neglecting the Basics of Cybersecurity While Increasing Complexity
- Blog
FrontJacking: A New Attack That Threatens Reverse Proxy Servers
- Blog
Meet Cye’s Chief of Critical Cyber Operations
- Blog
What You Need to Know About the NIST Cybersecurity Framework
- Blog
Cyber Risk Quantification vs. Cyber Risk Optimization
- Blog
What We Can Learn from the City of Dallas Ransomware Attack
- Blog
How Cye Optimizes Your Cybersecurity Budget
- Blog
What CISOs Can Gain from Cyber Risk Quantification
- Blog
What You Need to Know About the Anonymous Sudan Hacker Group
- Blog
3 Ways Hackers Successfully Breach Organizations
- Blog
Top 3 Considerations When Relying on Cyber Insurance
- Blog
Cyber Risk Assessment: What It Is and Why It’s Necessary
- Blog
Why SVB’s Closure Means More Security Risks for Its Customers
- Blog
3 Ways Red Team Services Help Protect Your Business’s Cyber Assets
- Blog
Building a Modern Red Team Infrastructure
- Blog
Insights from Recent Airport Cyberattacks: What We Learned
- Blog
6 Important Lessons Learned from an Incident Response
- Blog
Cyber Talks: Two Leaders Talk About Security in 2023
- Blog
Why ChatGPT is an Opportunity and a Threat to Cybersecurity
- Blog
Meet a Red Team Services Leader at Cye
- Blog
Addressing the Significant Challenges of OT Environment Security
- Blog
How to Perform a Cyber Risk Assessment in 2023
- Blog
Top 5 Cybersecurity Predictions for 2023
- Blog
Improving Security in Your OT Environments
- Blog
Meet Ira Winkler: Cye’s Newest Field CISO
- Blog
4 Key Strategies to Improve Your Company’s Cybersecurity
- Blog
Is Apache Commons Text RCE the New Log4Shell?
- Blog
The Top 3 Approaches of Cyber Risk Assessment Software
- Blog
The Top 3 Targets of Healthcare Cybersecurity Breaches
- Blog
Cyber Risk Assessment Services in the Financial Industry: 5 Key Tactics
- Blog
Traditional Cyber Risk Quantification Models Don’t Work. Here’s Why.
- Blog
The Top Healthcare Cybersecurity Trends for Hospital CISOs
- Blog
What Should a Cyber Risk Quantification Strategy Entail?
- Blog
Takeaways from 5 Real-World Healthcare Cybersecurity Breaches from 2022
- Blog
Top 5 Security Tips to Protect Social Media Profiles
- Blog
Using Cye Platform’s Mitigation Planner Graph for Actionable Insights
- Blog
3 Security Questions Your Board Might Ask
- Blog
Protecting Your Business from Attacks That Exploit Human Weaknesses
- Blog
Top Attacking Tools: Have You Attacked Your Own Network Yet?
- Blog
Russian Cyber Attacks: Analysis and Recommendations [Updated 22.5]
- Blog
Lapsus$ Attack on OKTA – Analysis and Recommendations
- Blog
The Possible China Taiwan Effect From The Russia Ukraine War
- Blog
Cyber Terrorism is Officially a Component of Warfare
- Blog
Yet Another Lesson on How Patience is a Virtue
- Blog
The Russia-Ukraine Cyber Attacks
- Blog
The Cyber Chapter of The Russian Playbook In Ukraine
- Blog
Application Security at Hyper-Growth Companies
- Blog
Log4Shell: Pragmatic Recommendations For CISOs
- Blog
Top 3 Cyber Threats and Challenges in 2022
- Blog
10 Tips for National Cybersecurity Awareness Month
- Blog
The 5 Security Gaps Most Organizations Will Face
- Blog
Making Sense of the TSA’s Latest Cyber Regulations for LNG Facilities
- Blog
Cye Partners with OTORIO to Combat Rise in Industrial Ransomware Attacks
- Blog
Your Cybersecurity Program Needs Data, Numbers and Facts
- Blog
Your Security Metrics are Making you Less Secure
- Blog
Cye Partners with ALSO to Arm SMEs with Enterprise-Level Cybersecurity
- Blog
Top 5 Cybersecurity Risks for Food Manufacturers
- Blog
Your Scanners and WAFs are Not Going to Protect You
- Blog
Board Members, Start Asking the Right Questions on Security
- Blog
Cybersecurity Maturity – A Game Changer in Due Diligence and M&A’s
- Blog
The Shocking Blind Spots Most CISOs Have in Their Networks
- Blog
We Welcome Our New Advisory Board to Support Our Global Growth
- Blog
The Biggest Mistakes Online Gaming CISOs are Making
- Blog
We Secured Over $100 Million Funding Round
- Blog
Real Cybersecurity: What You Get When You Eliminate the Guesswork
- Blog
A Glimpse into the Minds of Cyber Experts
- Blog
Redefining Cybersecurity in the 2021 Post-Corona Paradigm
- Blog
How Insurers are Combating Ransomware Hackers
- Blog
IoMT Threats: Addressing Digital Medical Device Cybersecurity
- Blog
The Use of Too Many Security Solutions has Become a Security Problem
- Blog
Protect Me from Myself: The Human Factor in IT Security
- Blog
Automotive Cybersecurity: The Day After Covid-19
- Blog
What Makes Us CYE – The Five Lights that Guide Our Way
- Blog
Cybersecurity Best Practices for South African Organizations
- Blog
Cye Partners With Zurich Insurance